The UAE has become a major hub for financial technology, with fintech firms operating across payments, digital finance, investment services, lending, and other technology-enabled financial activities.
But growth creates a regulatory question that every senior compliance and risk professional should be able to answer:
Where does regulatory exposure begin?
For a fintech, the answer is rarely found in one regulation or one compliance policy. Exposure can begin with the business model itself—its products, customers, activities, technology, jurisdictions, and operating structure.
This makes fintech compliance more than a documentation exercise. It requires a clear understanding of which regulatory requirements apply, how risks are managed, and whether the compliance function is equipped to support the business as it develops.
The issue is becoming more relevant as regulators increase their focus on how fintech firms operate their compliance functions. In April 2026, the Dubai Financial Services Authority (DFSA) published a thematic review of compliance arrangements across fintech firms in the Dubai International Financial Centre (DIFC). The review identified recurring themes relating to compliance resources, outsourcing, governance, technology adoption, and regulatory engagement. (Dubai Financial Services Authority [DFSA], 2026).
Where Does Regulatory Exposure Begin for a Fintech in the UAE?
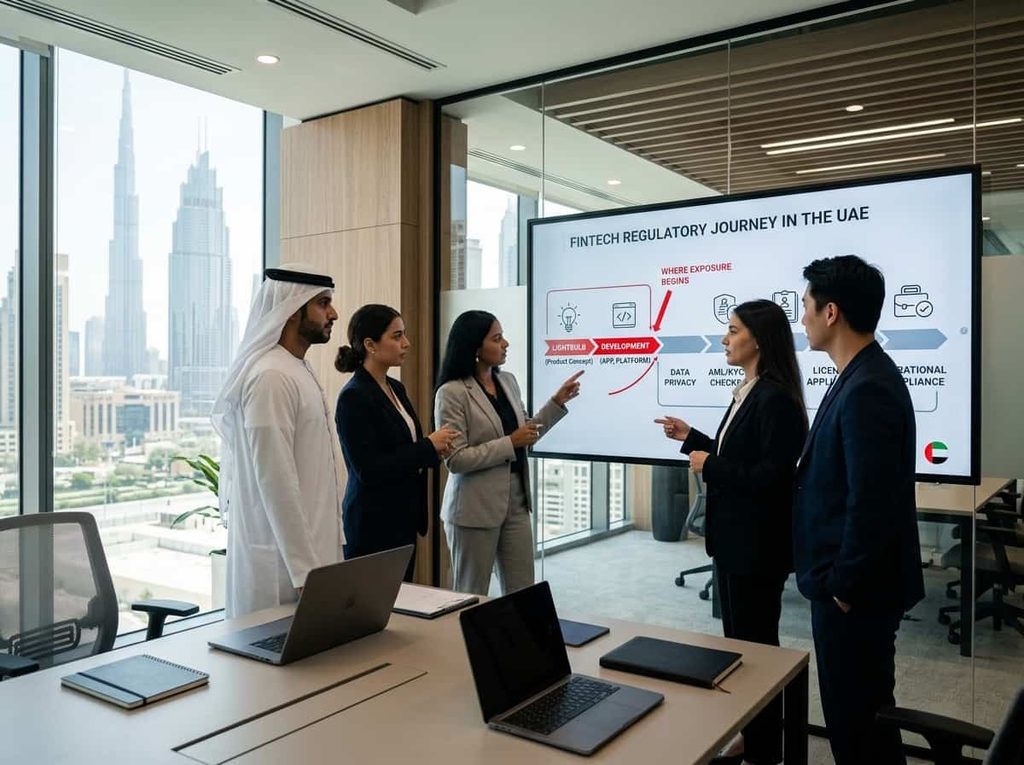
Regulatory exposure often begins before a policy is written.
It starts with understanding what the business actually does.
A fintech may provide payment services, operate a digital platform, facilitate investments, provide technology to regulated institutions, or conduct activities connected to virtual assets. These activities can create different regulatory obligations.
The Business Model Comes Before the Compliance Framework
A compliance framework should reflect the business it is designed to govern.
Before determining the appropriate controls, a fintech should consider:
- What services does the business provide?
- Who are its customers?
- Where are customers located?
- How do funds and transactions move?
- What financial crime risks exist?
- Which third parties support critical activities?
- What technology is used for onboarding and monitoring?
- Which jurisdictions are involved?
These questions help establish the firm’s regulatory perimeter.
Starting with generic policies without first understanding the business can create a framework that looks complete but does not properly address the firm’s actual risks.
Understanding the UAE Regulatory Perimeter
The UAE does not have one identical regulatory framework for every fintech.
The applicable requirements depend on the firm’s activities, regulatory status, and where those activities are conducted.
For example, firms operating within the DIFC may fall under the DFSA framework, while relevant financial institutions operating under the UAE federal financial system may be subject to Central Bank of the UAE (CBUAE) requirements.
The first step should therefore be to identify the regulatory framework relevant to the firm’s actual activities.
When Technology Creates Additional Compliance Questions
Technology can change how financial services are delivered, but it does not remove the underlying compliance responsibility.
Digital onboarding, automated processes, APIs, cloud services, artificial intelligence, and digital identity solutions can introduce additional questions around identity verification, data, governance, monitoring, and operational risk.
CBUAE guidance permits financial institutions to use technology-neutral approaches to customer identification and verification, including digital identification methods, provided the systems rely on reliable and independent sources and are supported by adequate governance, processes, and risk controls. (Central Bank of the UAE [CBUAE], 2025).
For fintech firms, technology should therefore be considered part of the control environment rather than treated as a separate issue.
Fintech Compliance: What Regulatory Requirements Should Firms Understand in the UAE?
Once the regulatory perimeter is clear, the next question is how the firm should structure its fintech compliance arrangements.
The exact requirements vary by business model and regulatory status, but several areas deserve particular attention.
AML/CFT and Financial Crime Controls
Anti-money laundering and counter-terrorist financing controls should reflect the firm’s actual risk profile.
Relevant factors may include customer types, products, transaction activity, jurisdictions, delivery channels, ownership structures, and third-party relationships.
A risk-based approach allows the firm to determine where stronger controls are needed rather than applying the same measures to every customer or activity.
The CBUAE identifies risk-based CDD, KYC, recordkeeping, and financial crime controls as fundamental elements of compliance for relevant licensed financial institutions. (CBUAE, 2025).
The practical question is whether those controls work in the operating environment—not simply whether the policy exists.
KYC, CDD and Beneficial Ownership
Know Your Customer (KYC) and Customer Due Diligence (CDD) are central to financial crime compliance.
For relevant CBUAE-supervised institutions, CDD includes customer identification and verification, beneficial ownership, understanding the purpose and nature of the relationship, and ongoing monitoring.
For fintechs, KYC should therefore not be treated as a one-time onboarding exercise.
Customer activity can change. Ownership can change. Risk can change.
The compliance framework needs to account for those changes through ongoing monitoring and periodic or event-driven reviews.
Governance and Compliance Accountability
A strong compliance function needs clear responsibilities and appropriate access to senior management.
This becomes particularly important as fintech grows.
The DFSA’s 2026 thematic review found that 53% of the reviewed fintech firms had three or fewer compliance staff, with some relying on a single individual. It also identified governance weaknesses and overlapping roles in some firms. (DFSA, 2026).
A small compliance team is not automatically a weakness. Proportionality matters.
The question is whether the firm’s resources, reporting lines, independence, and expertise remain appropriate for its size, complexity, and risk exposure.
Outsourcing Does Not Remove Accountability
Outsourcing can provide specialist expertise and additional capacity, but it does not remove the need for effective oversight.
A fintech should understand what is being outsourced, who remains accountable, how performance is monitored, and how issues are escalated.
The DFSA’s review found that nearly 58% of the fintech firms assessed outsourced compliance functions and highlighted concerns in some cases around local oversight and responsiveness. (DFSA, 2026).
The objective should be controlled use of external expertise—not the transfer of accountability.
How Should a Fintech Assess Its Regulatory Compliance Position?
Understanding the requirements is only the beginning.
Senior management should also ask whether the existing compliance framework is properly designed and operating as intended.
A practical assessment can follow four steps:
| Step | What It Involves |
| 1. Map the Business and Regulatory Obligations | Identify products, services, customers, jurisdictions, transaction flows, technology, and third-party relationships. |
| 2. Assess Existing Controls | Review AML/KYC, CDD, transaction monitoring, governance, reporting, training, recordkeeping, and compliance testing. |
| 3. Identify and Prioritise Gaps | Ensure material gaps have clear ownership, defined remediation priorities, and appropriate management oversight. |
| 4. Keep the Framework Under Review | Regularly reassess products, technology, customers, risks, and regulatory expectations to maintain an effective and responsive compliance framework. |
Regulatory Compliance Advisory for Fintech Firms in the UAE
For fintech firms operating in the UAE, regulatory compliance requires more than knowing the relevant rules.
It requires understanding how those rules apply to the firm’s business model and whether its compliance arrangements are proportionate, operational, and defensible.
Mukhtara Compliance provides regulatory compliance services to financial institutions, fintechs, and regulated entities across the UAE, GCC, and wider MENA region. Its work includes regulatory gap analysis, compliance framework design, AML/KYC programme development, enterprise risk assessment, ongoing risk monitoring, and CISI-accredited training.
Where Specialist Advisory Can Add Value
Specialist support can help firms assess:
- Regulatory perimeter and obligations
- AML/KYC frameworks
- Compliance governance
- Regulatory and enterprise risk
- Control gaps
- Compliance resourcing
- Regulatory readiness
- Ongoing monitoring and remediation
The objective is not to add unnecessary documentation. It is to establish whether the compliance framework is appropriate for the business and capable of evolving with it.
Speak With Mukhtara About Your Fintech’s Regulatory Position
Regulatory questions are best addressed before they become regulatory problems.
If your fintech is entering the UAE market, expanding its activities, reviewing its compliance function, or assessing gaps in its existing framework, Mukhtara Compliance can help you establish where your regulatory exposure sits and what requires attention.
Start with a regulatory gap analysis and assess your current framework against the obligations relevant to your business.